How North Korean Hackers Target IT Professionals
North Korean hackers belonging to the state-sponsored cyber espionage group known as ‘WaterPlum’ have compromised at least 30,000 computers across more than 100 countries in a massive global cyberattack. According to the FBI, the malicious campaign took place between December of last year and July, specifically targeting software developers and IT professionals in the United States, Japan, and Europe through sophisticated social engineering tactics.
The Fake Job Interview Malware Scam
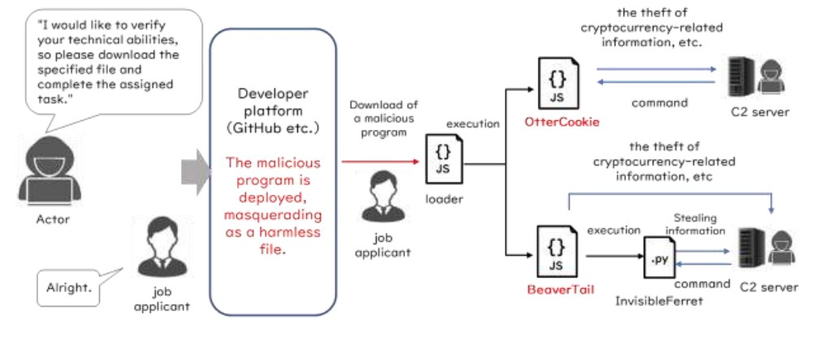
The attackers disguised themselves as recruiters, AI firms, cryptocurrency projects, and NFT startups on social media and freelance platforms. During online job interviews and coding tests, the threat actors tricked unsuspecting applicants into downloading malicious files or executing fraudulent programs under the guise of fixing video conferencing errors. Once installed, the malware captured keystrokes, passwords, screen captures, and sensitive personal identification documents including passports and driver’s licenses.
Cryptocurrency Theft and Financial Losses
The primary objective of the campaign was financial gain, with the hackers targeting private keys and recovery phrases for crypto wallets. FBI findings indicate that WaterPlum successfully compromised over 7,000 cryptocurrency wallets, stealing at least $10.71 million USD in digital assets. US authorities believe the WaterPlum group and associated North Korean IT personnel operate under the 313th Bureau of the Munitions Industry Department of the Workers’ Party of Korea.