A PHP vulnerability has security experts on high alert as cyber threat actors prepare potential large-scale attacks targeting government and financial institutions worldwide using a newly uncovered flaw.
Understanding the PHP Security Flaw and Attack Preparations
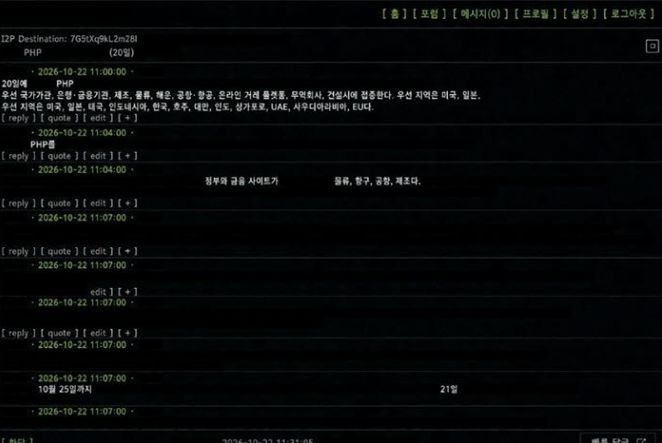
Recent reports reveal that attackers utilizing the Korean language and tactics resembling advanced persistent threat groups have been spotted discussing exploits via anonymous networks. The flaw, designated informally as ‘PHP2Shell’, allows unauthorized remote command execution and data extraction without requiring user login, posing massive risks to web infrastructure globally.
Target Sectors and Potential Lazarus Group Link
Preliminary investigations by cybersecurity firms indicate that primary targets include government agencies, banks, financial institutions, manufacturing, logistics, and transportation companies across multiple nations. Although tactical similarities point toward the North Korean-linked hacking group Lazarus, definitive evidence confirming a direct connection remains under investigation.
Global Response and Official Patches
In response to the escalating threats, the PHP development team has released critical security updates to resolve the vulnerability. Government ministries and internet security agencies have subsequently issued advisory warnings, urging organizations to apply patches immediately and monitor systems closely for unauthorized activities.